
Identity and access
Design login, role, service-account, and ownership models that avoid broad standing privileges.
Protect data through layered controls
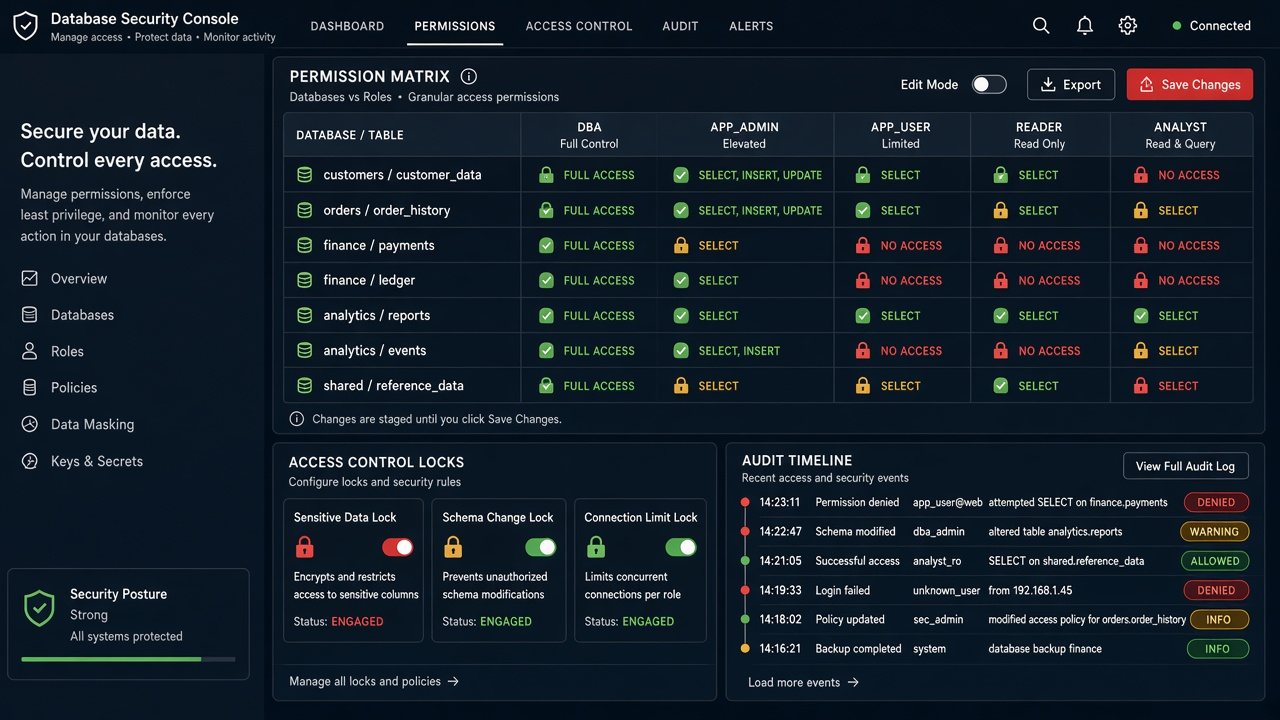
Database security connects identity, permissions, application access, network boundaries, encryption, auditing, and operational review. The goal is to grant each person and service only what it needs while preserving a clear record of sensitive activity.
Core focus
Design login, role, service-account, and ownership models that avoid broad standing privileges.
Apply encryption, masking, row-level controls, secret management, and secure connection settings where the data requires them.
Capture important activity, review privileged access, test controls, and retain evidence for security and compliance reviews.
Typical work
Results